Skip to content

Capability / 02

Security engineered into every layer.

PACSAL (Programming, Advanced Cyber-Security & Automation Lab) builds practical cyber-security tools, secure architectures, and defensive systems designed to reduce risk before it becomes operational damage.

We focus on real-world security solutions that are usable, repeatable, and built into the system from the start.

AssessDefendDetectAdvance

  • Application

    Scan · Validate · Protect

  • Dependencies

    Analyze · Monitor · Alert

  • Infrastructure

    Secure · Harden · Observe

  • Network

    Monitor · Detect · Respond

Threat Scan

Sample
Scanning...Complete100%
  • Vulnerabilities3
  • Warnings7
  • Info12

System secure

Security Areas

Comprehensive security engineering.

From architecture to monitoring, PACSAL (Programming, Advanced Cyber-Security & Automation Lab) builds security into every stage of the system lifecycle.

Practical securityfor real systems.
  • Secure Architecture

    Design systems with security in mind from the beginning.

  • Application Security

    Identify and fix weaknesses in application logic and behavior.

  • Code & Dependency Analysis

    Scan, analyze, and reduce software supply-chain risk.

  • Security Tooling

    Practical tools for developers and engineering teams.

  • Threat Analysis

    Understand exposure, attack paths, and realistic security risks.

  • Monitoring & Detection

    Detect important security events before they become incidents.

  • Security Automation

    Automate repeatable security checks and operational workflows.

  • Hardening

    Reduce unnecessary exposure and strengthen system configuration.

Security Philosophy

Security is not a final checklist.

Security decisions made during architecture and implementation are easier to control, easier to verify, and far more effective than late-stage remediation.

  1. 01

    Reduce Attack Surface

    Minimize risk through clear architecture, configuration control, and dependency discipline.

  2. 02

    Verify Assumptions

    Test, analyze, and validate trust boundaries, system behavior, and critical dependencies.

  3. 03

    Continuously Validate

    Security is an ongoing process, not a one-time effort.

Featured Project

CyberTool.dev

Security research in practice.

A developer-focused cyber-security platform for code scanning, practical findings, and accessible security workflows.

CyberTool.dev reflects PACSAL (Programming, Advanced Cyber-Security & Automation Lab)'s focus on practical security tooling that helps developers understand problems clearly and act on useful findings.

  • Repository scanning
  • Developer focused
  • Continuously evolving
  • Built as part of PACSAL (Programming, Advanced Cyber-Security & Automation Lab) Labs
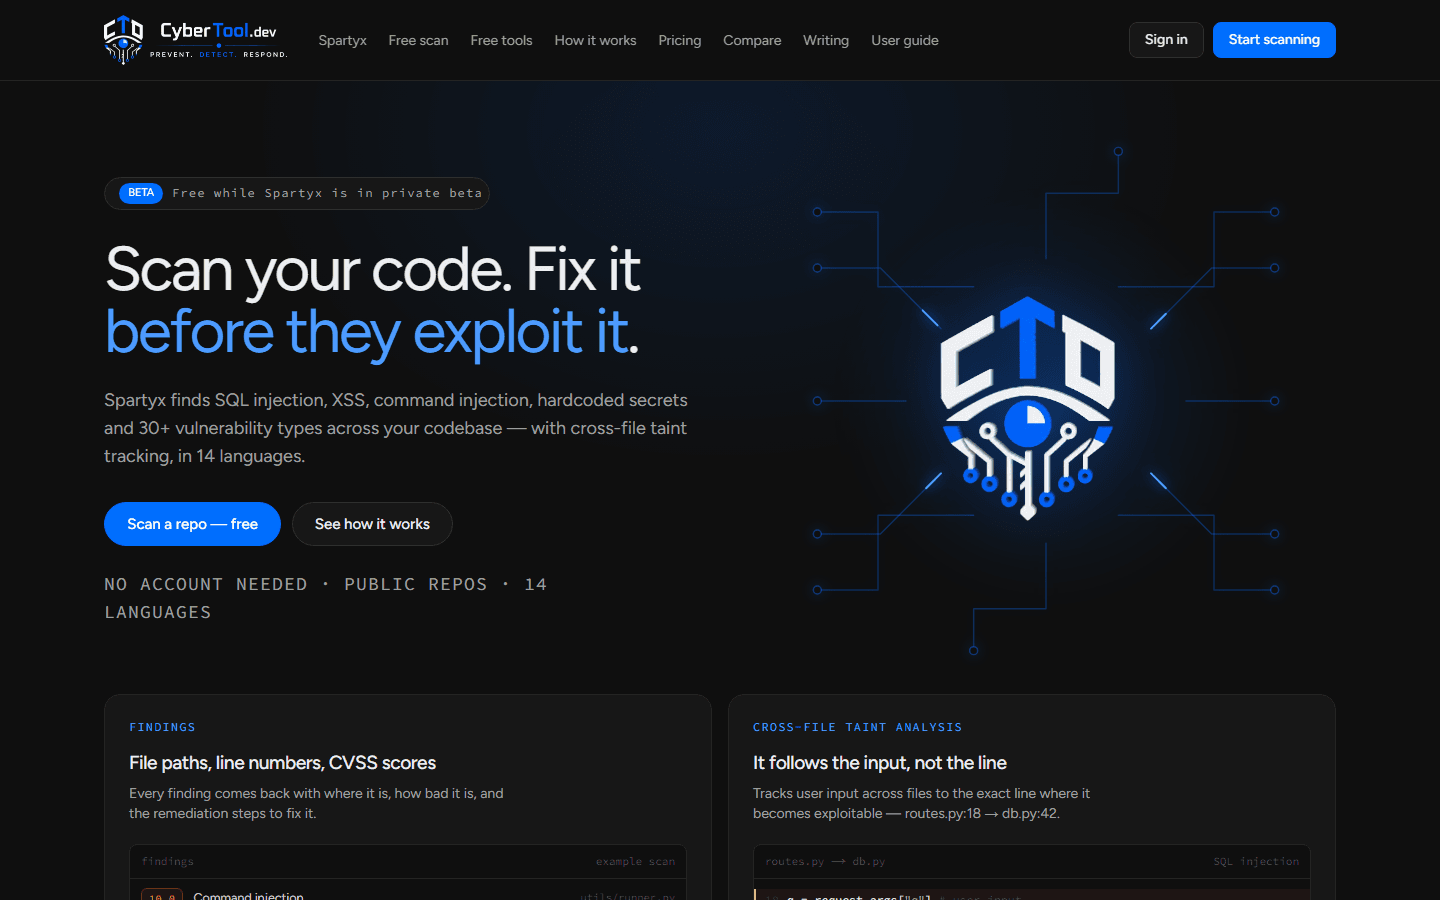
CyberTool.dev home page: scan your code and fix it before it is exploited

Security Process

A practical approach to security.

Integrated into the development and operational lifecycle.

Build a moreresilient tomorrow.
  1. 01

    Discover

    Understand the system, assets, attack surface, and risk.

  2. 02

    Analyze

    Assess code, dependencies, configuration, and architecture.

  3. 03

    Secure

    Implement controls and reduce unnecessary risk.

  4. 04

    Monitor

    Detect issues and abnormal behavior.

  5. 05

    Automate

    Reduce manual effort and improve consistency.

  6. 06

    Improve

    Learn from findings and strengthen the system.

Technology & Methods

Tools and techniques we use.

Selected for practical, real-world security work.

  • Security Analysis

    • Static Analysis
    • Dependency Scanning
    • Code Review
    • Configuration Review
  • Infrastructure

    • Linux
    • Docker
    • System Hardening
    • Network Security
  • Languages & Tools

    • Python
    • Rust
    • Bash
    • Custom Tooling
  • Monitoring

    • Logging
    • Alerting
    • Anomaly Detection
    • Incident Analysis
  • Automation

    • Security Workflows
    • CI/CD Integration
    • Automated Scanning
    • Scheduled Tasks

Insights

View All Insights

Latest from our research.

Real-World Application

Security across the system lifecycle.

Security supports every stage — from development to deployment and operations.

  1. Development

    • Secure coding
    • Dependency checks
  2. Build & Test

    • Automated scanning
    • Security validation
  3. Deployment

    • Hardened environments
    • Access control
  4. Operations

    • Monitoring & detection
    • Incident response

Let's secure what's next

Build security into the system before it becomes a problem.

Tell PACSAL (Programming, Advanced Cyber-Security & Automation Lab) about your security requirements. We'd love to help.